Your Company Could Already Be on a Leak Site - Would You Know?
We monitor the dark web, ransomware leak sites, and dozens of other threat feeds around the clock for every company you track - and surface it the moment you look at that company in OSINT or External Exposure Assessments, evidence and screenshots included.
Somewhere right now, a ransomware crew is publishing a fresh batch of victim names on their own leak site. A breach outlet is writing up an incident from last week. A botnet tracker is quietly logging which IPs just joined a command-and-control network. None of it is hidden. All of it is public. And almost nobody is watching all of it, continuously, for the companies they actually care about.
We are.
We never stop watching
Pentesterra runs a standing dark web and threat intelligence monitor behind every company you track - ransomware leak sites, breach disclosure outlets, botnet and command-and-control infrastructure, malicious certificate fingerprints, and a growing list of other sources we keep adding to. We don't publish the full list, and we don't need to: what matters is that it runs around the clock, refreshes on a schedule, and checks every company the moment you add it - not once, but again every time the feeds update.
This is exactly the kind of signal that usually reaches a company far too late
- from a journalist, a customer, or a regulator, instead of from their own security team. We'd rather you find out from us, first.
It's not buried in a report - it's right where you're already looking
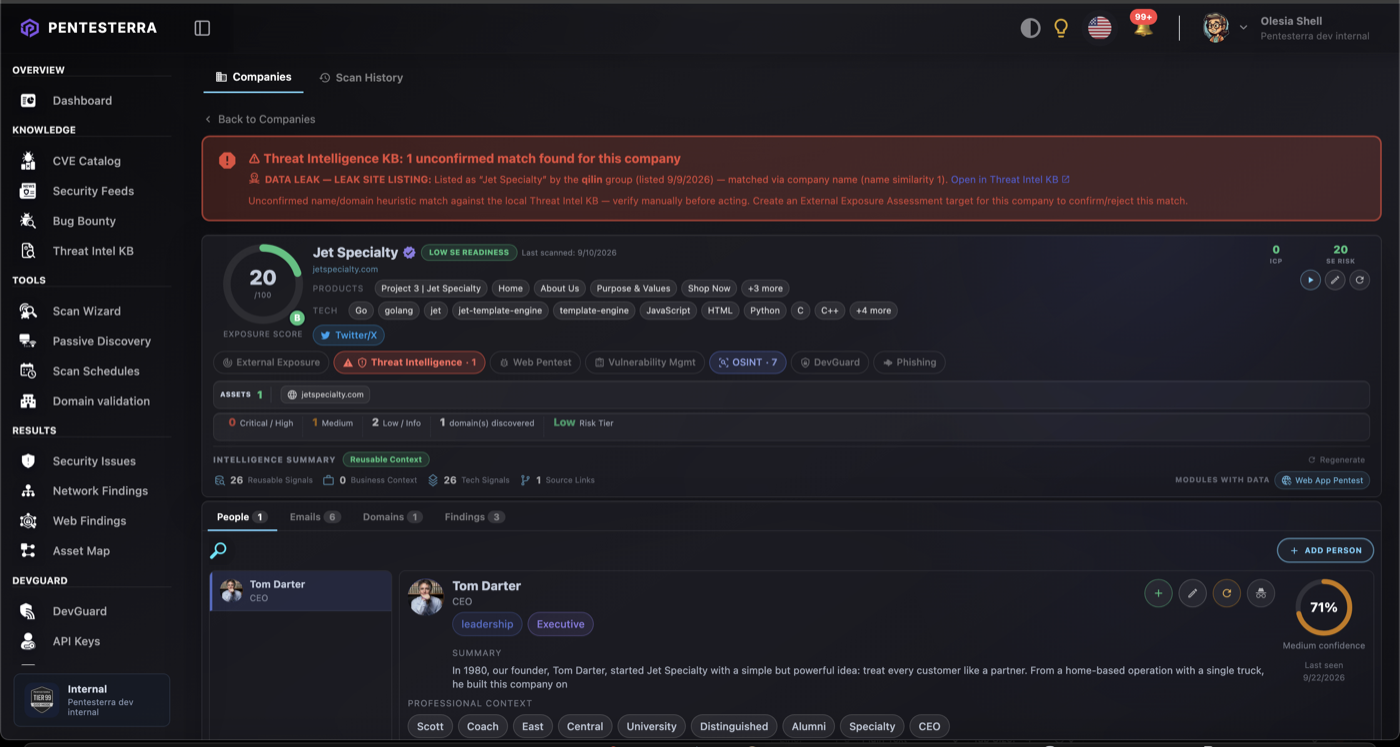
Most threat intel stays locked inside a dashboard nobody opens until something already went wrong. We did the opposite: open any company in OSINT, and if our monitor has found a match, it's already there - no separate search, no second tool, no remembering to check.
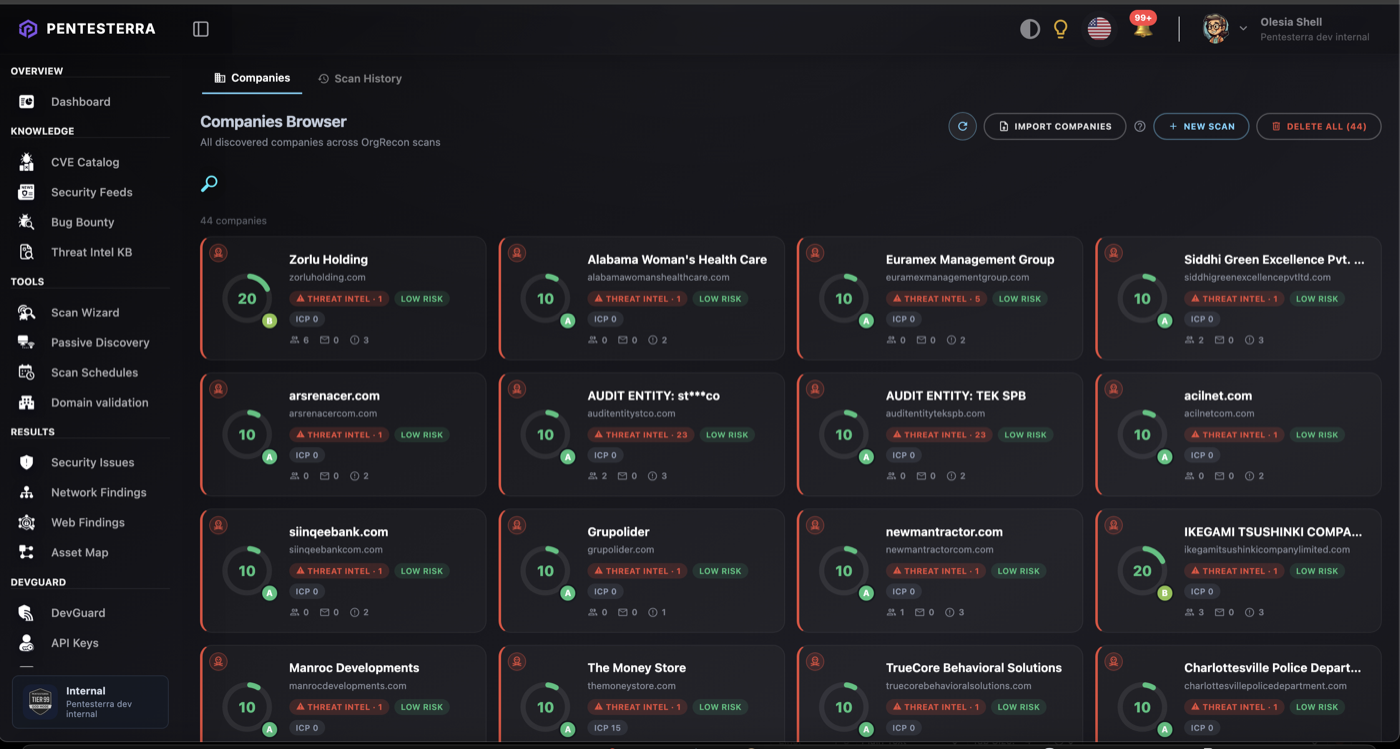
That same red flag is visible at a glance across your entire portfolio - scroll through hundreds of companies and the ones with a real signal jump out immediately. The exact same intelligence is wired into External Exposure Assessments too, so wherever you opened a company from, you see the same story.
We don't only match on the company name, either. A leak-site post or a breach headline sometimes names a person instead - a founder, an executive. Our monitor checks against the people we've profiled around that company too, and tells you exactly who and where it matched.
Real evidence, not a guess
Every match comes with a receipt. We show you the ransomware group, the sector, the date it was posted - and where the leak site itself published one, the original screenshot of the post, pulled straight from the source:
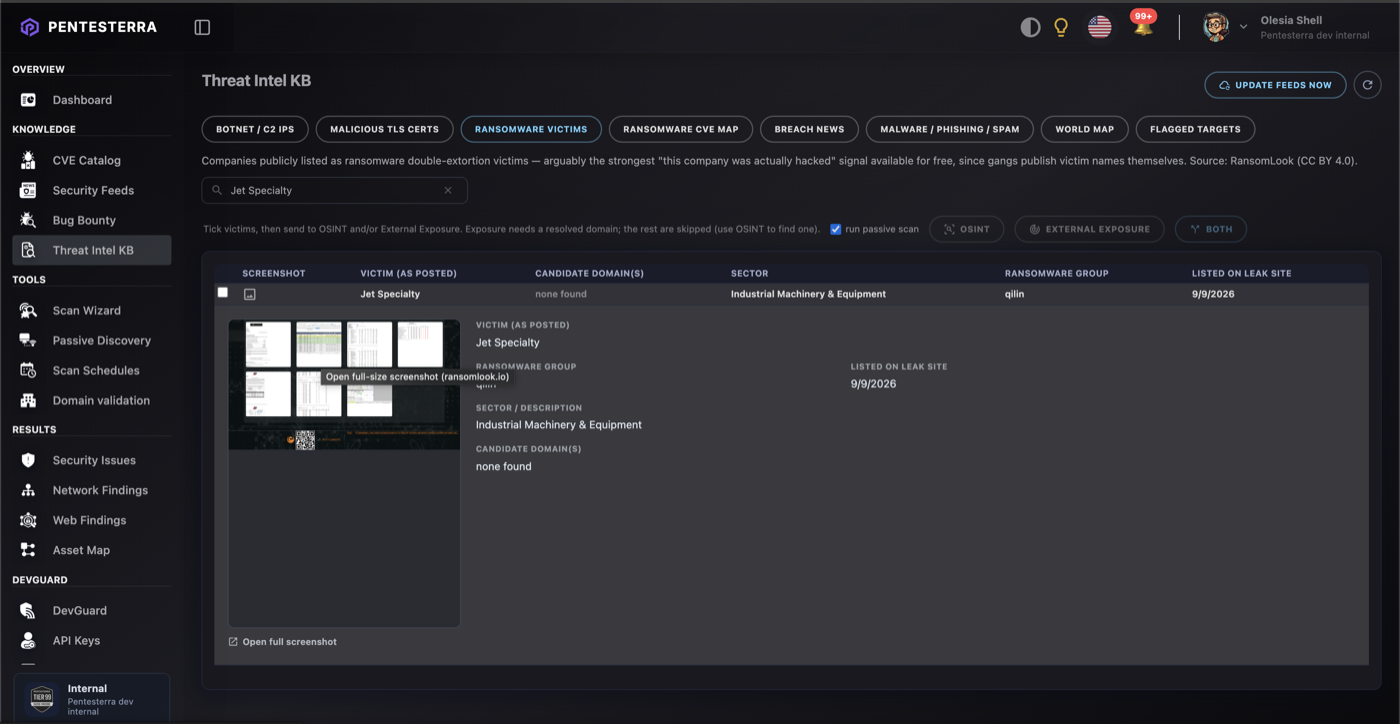
Our correlation engine cross-checks a match through multiple independent signals - not a single guess, but the same kind of evidence you'd assemble yourself if you had the time to dig through every source by hand. One click takes you from the flag straight to that evidence, no manual digging required.
Built to triage thousands, not just the one you're staring at
This only matters if it scales past the one company you happen to have open. Our Threat Intel KB is a live, searchable worklist - tick the victims and breach mentions relevant to you and push the selection straight into OSINT and/or External Exposure Assessments in bulk, with a passive scan queued automatically:
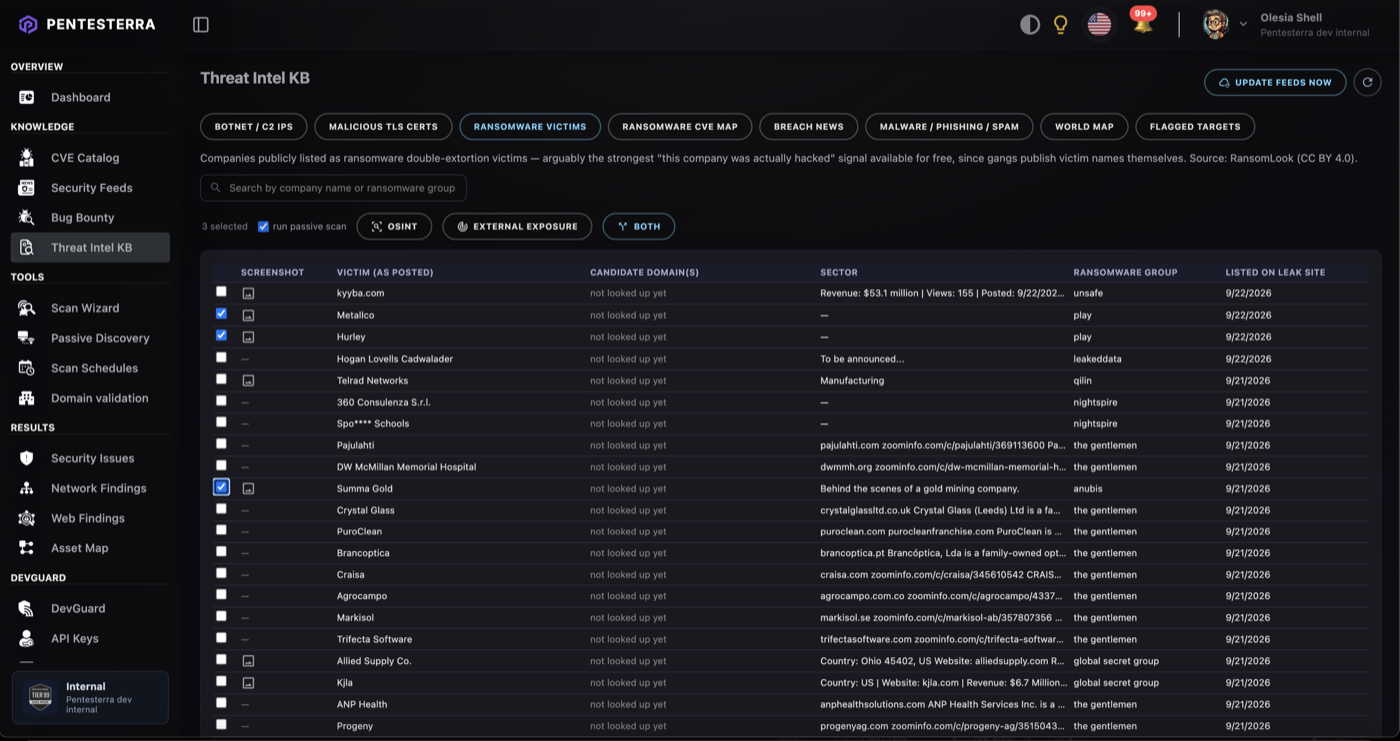
It's the same engine behind our bulk External Exposure workflow: upload thousands of companies at once, and every single one gets checked against this exact monitoring - not just the handful you remembered to look up yourself.
Why this actually matters to you
A real threat picture isn't one signal - it's OSINT, dark web monitoring, and Threat Intel KB correlation working together, because a company can be exposed in a dozen different ways at once and any one of them alone tells you only part of the story. Whether you're screening a vendor before you sign a contract, keeping an eye on your own attack surface, or checking whether a client just became a headline, this is exactly the layer of visibility you need before you find out the hard way - already built in, already watching, already there the moment you open the company.
https://pentesterra.com/blog/dark-web-ransomware-leak-monitoring-threat-intel-everywhere